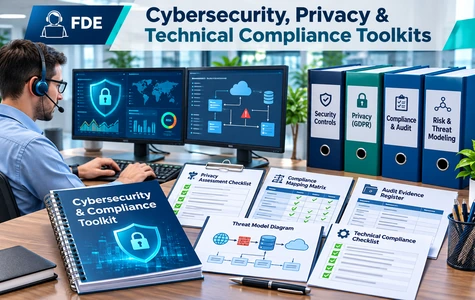
Security and privacy are engineering responsibilities throughout the lifecycle of customer-facing applications, AI systems and industrial environments. The Cybersecurity, Privacy & Technical Compliance Toolkits bring together practical resources for Forward Deployed Engineers and enterprise specialists who must review technical risks and document controls before and during delivery.
Across 9 focused parts and 57 indexed files, this toolkit addresses threat modeling and trust boundaries; identity, keys and access; OT/ICS and cyber-physical interfaces; data classification and privacy; application and API testing; supply-chain assurance; jurisdictional control evidence; AI agent and model security; and incident triage, containment and escalation.
The index includes Word guides, Excel control matrices, Draw.io diagrams, Python practice labs, JSON/JSONL fixtures and a training lab ZIP. Teams can tailor the working materials to their architectures and obligations, perform approved security reviews, and use synthetic training scenarios without treating the sample files as production-certified security solutions.
- Strengthen security architecture reviews with threat-modeling guidance, STRIDE scenarios, trust-boundary diagrams and control coverage checklists.
- Improve identity and OT/ICS safeguards using least-privilege design, access and key lifecycle reviews, industrial remote-access assessment and safety-security boundaries.
- Embed privacy and secure processing controls through data classification, retention and minimization checks, cross-border transfer reviews and synthetic data-masking labs.
- Support application, API and supply-chain assurance with technical test catalogs, remediation evidence, dependency risk reviews, sample SBOM data and controlled exercises.
- Prepare evidence and incident decisions using compliance mapping, AI agent security evaluation, incident severity criteria, containment checklists and security handoff diagrams.
Below is the complete inventory from the supplied Index 13: 57 resources across 9 parts, including DOC, XLS, Draw.io, JSON, Python, ZIP and JSONL files.
| Type | Files List |
|---|---|
| Secure_Architecture_Threat_Modeling_Guide.doc | |
| Threat_Model_Review_Procedure.doc | |
| Industrial_Application_Threat_Cases.doc | |
| Threat_Scenario_and_STRIDE_Matrix.xls | |
| Threat_Control_Coverage_Checklist.xls | |
| System_Trust_Boundary_Diagram.drawio | |
| Identity_Access_Management_Control_Standard.doc | |
| IAM_Architecture_Exercise.doc | |
| Least_Privilege_Role_Design.xls | |
| Key_Secrets_Lifecycle_Checklist.xls | |
| Access_Rights_Review_Scenarios.xls | |
| Privilege_Escalation_Simulation.json | |
| OT_ICS_Security_Assessment_Playbook.doc | |
| OT_Cyber_Physical_Hazard_Casebook.doc | |
| Industrial_Remote_Access_Exposure_Review.xls | |
| OT_Patch_Exception_and_Maintenance_Window_Matrix.xls | |
| OT_Safety_Security_Approval_Boundaries.xls | |
| OT_Zone_Conduit_Trust_Diagram.drawio | |
| Data_Handling_Policy_Drafting_Exercise.doc | |
| Privacy_Requirement_Validation_Casebook.doc | |
| Privacy_Impact_Assessment_and_Approval_Template.doc | |
| Sensitive_Data_Classification_Register.xls | |
| Retention_Minimization_Control_Checklist.xls | |
| Cross_Border_Data_Transfer_Jurisdictional_Review_Matrix.xls | |
| Privacy_Data_Flow_And_Trust_Model.drawio | |
| Data_Masking_Synthetic_Lab.py | |
| Secure_Application_Test_Procedure.doc | |
| Security_Test_Case_Catalog.xls | |
| Secure_Code_Fix_Review.xls | |
| Remediation_Evidence_Checklist.xls | |
| API_Abuse_Test_Suite.py | |
| Security_Regressions_Fixtures.json | |
| Vulnerable_Training_App_Lab.zip | |
| Software_Supply_Chain_Assurance_Guide.doc | |
| Dependency_Update_Threat_Simulation.doc | |
| Open_Source_Dependency_Risk_Scorecard.xls | |
| Supplier_Artifact_Assurance_Checklist.xls | |
| Vulnerability_Triage_Exercise.xls | |
| Software_Bill_Of_Materials_Fixture.json | |
| Security_Requirement_and_Evidence_Mapping_Guide.doc | |
| Security_Evidence_Exception_Casebook.doc | |
| Jurisdiction_Security_Obligation_Applicability_Matrix.xls | |
| Security_Control_Implementation_Evidence_Index.xls | |
| Security_Assurance_Supplier_Attestation_Review.xls | |
| Model_Data_Exfiltration_Simulation.doc | |
| AI_Agent_Security_Test_Catalog.xls | |
| Agent_Security_Control_Review.xls | |
| AI_Security_Findings_Closure_Workbook.xls | |
| Agent_Security_Threat_Model.drawio | |
| Tool_Authorization_Abuse_Test_Lab.py | |
| Prompt_Injection_Adversarial_Fixtures.jsonl | |
| Security_Incident_Triage_Containment_and_Forensic_Evidence_Procedure.doc | |
| Sensitive_Data_Exposure_Decision_and_Legal_Referral_Record.doc | |
| Security_Incident_Tabletop_Casebook.doc | |
| Security_Incident_Severity_and_Customer_Notification_Matrix.xls | |
| Security_Incident_Containment_and_Recovery_Checklist.xls | |
| Incident_SRE_to_Security_Handoff_Sequence.drawio | |
Price: $47.00

Secure payment via PayPal. Instant digital delivery after successful payment.
| Date File Updated | 10/04/2025 |
|---|---|
| File Format | doc, xls, drawio, json, py, zip, jsonl |
| No. of files | 57 Files, 9 Folders |
| File download size | 3.02 MB (.rar) |
| Language | English |
This document has been certified by a professional
100% customizable. You can edit our templates as needed.
Instant download after completing your order.
We recommend downloading this file onto your computer.
Your payment information is processed securely.
After payment, if you require an invoice, please email us.
Support contact: supports@it-toolkits.org
Build security, privacy and technical assurance into every engineering engagement
Practical guides, review matrices, trust-boundary diagrams and controlled labs for threat modeling, IAM, OT/ICS security, privacy, API assurance, AI agent security and incident response.
1. Who is the Cybersecurity, Privacy & Technical Compliance Toolkit designed for?
It is intended for Forward Deployed Engineers, security architects, application and cloud security specialists, privacy engineers, OT/ICS security teams, compliance managers and technical delivery leaders reviewing enterprise and customer-facing systems.
2. What is covered by the toolkit?
The nine parts cover security threat modeling, identity and access, OT/ICS cybersecurity, privacy and data processing, application and API security, software supply-chain assurance, technical compliance evidence, AI agent security, and security incident response.
3. How many files and which formats are listed?
Index 13 identifies 57 resources in 9 parts: 19 Word (.doc), 25 Excel (.xls), 5 Draw.io (.drawio), 3 JSON (.json), 3 Python (.py), 1 ZIP (.zip) and 1 JSON Lines (.jsonl) file.
4. Does the toolkit include security threat modeling and STRIDE?
Yes. Part 1 includes a security threat modeling guide, threat model review procedure, industrial attack scenarios, a Threat Scenario and STRIDE Matrix, control coverage checklist and trust-boundary diagram.
5. What identity and secrets management materials are included?
Part 2 contains an IAM control standard and architecture exercise, least-privilege role design, access-rights review scenarios, key and secrets lifecycle checklist, and a synthetic privilege-escalation simulation.
6. Does the toolkit address industrial control systems and cyber-physical safety?
Yes. Part 3 addresses OT/ICS security assessments, remote-access exposure, patch and maintenance exceptions, safety-security approval boundaries, and OT zone-conduit diagrams. Site-specific safety decisions require qualified engineering review.
7. Can I use the toolkit to review data privacy and data retention?
Part 4 includes data-handling policy exercises, privacy requirement cases, a privacy impact assessment and approval template, sensitive-data classification, retention/minimization checks and a cross-border jurisdictional review matrix.
8. Is a real-data masking solution included?
The index includes a Data Masking Synthetic Lab in Python for training and evaluation. It does not establish that any script is independently validated for live sensitive data. Review and test in approved environments before using production data.
9. Which application and API security testing resources are available?
Part 5 contains an application security test procedure, security test catalog, secure-code review, remediation evidence checklist, API abuse test suite, regression fixtures and a vulnerable training application lab.
10. Is the vulnerable training application intended for production use?
No. The Vulnerable Training App Lab is a practice resource. It should only be used in isolated, authorized environments and never exposed to customer or public production networks.
11. How are open-source dependencies and software supply-chain risks addressed?
Part 6 contains software supply-chain guidance, dependency threat simulations, open-source risk scorecards, supplier artifact checklists, vulnerability triage exercises and a sample Software Bill of Materials (SBOM) fixture.
12. Does the toolkit guarantee compliance with particular laws or standards?
No. Part 7 includes jurisdictional applicability and security-evidence mapping workbooks, but the index does not represent a certification or legal opinion. Applicable requirements must be validated by responsible compliance and legal teams for each deployment.
13. Can the files support security audits and control evidence collection?
Yes. The Security Control Implementation Evidence Index, jurisdictional obligation matrix, security assurance supplier attestation review and exception casebook provide structures for organizing evidence and review decisions.
14. Are AI agents, prompt injection and model abuse covered?
Part 8 includes an AI agent security test catalog, control review workbook, agent threat model, tool authorization abuse lab, prompt-injection fixtures and a model data exfiltration simulation, to support authorized security assessments.
15. How does the toolkit help incident response and customer escalation?
Part 9 lists incident triage and containment procedures, sensitive-data exposure decision records, tabletop cases, incident severity/customer notification matrices, containment and recovery checklists, and an SRE-to-security handoff diagram.
16. Can the resources be tailored to regulated and customer environments?
The templates can support tailoring to customer architecture, access roles, applicable obligations, supplier contracts and safety boundaries. Technical controls, legal conclusions and incident notification decisions require organization-specific approval.
17. What is the toolkit price and how do I pay?
The listed price is $47.00 USD. The two checkout forms are carried over unchanged from the website template; purchase instructions appear in the Payment Guide. Contact supports@it-toolkits.org for assistance.
18. Where can I review the full index or ask about file compatibility?
The complete list of 57 indexed files appears in the Toolkit Documents table. For questions about formats, editing software, current downloads or toolkit use, contact supports@it-toolkits.org.
Software & Application Engineering Toolkits
Integrate application engineering workflows with secure coding, code review and remediation practices.
Enterprise Systems & OT/IT Integration Toolkits
Map enterprise interfaces and operational technology dependencies that define integration trust boundaries.
Data Engineering & Analytics Toolkits
Extend privacy, classification and secure processing considerations into data pipelines and analytics.
AI, LLM & Agent Solution Engineering Toolkits
Align AI agent architecture, model evaluation and tool orchestration with security controls.
DevOps, CI/CD & Infrastructure Automation Toolkits
Connect software supply-chain assurance with pipeline controls, IaC reviews and build evidence.
Technical Governance, Risk & Decision Management Toolkits
Coordinate engineering risks, approvals, control exceptions and accountable technical decisions.


English